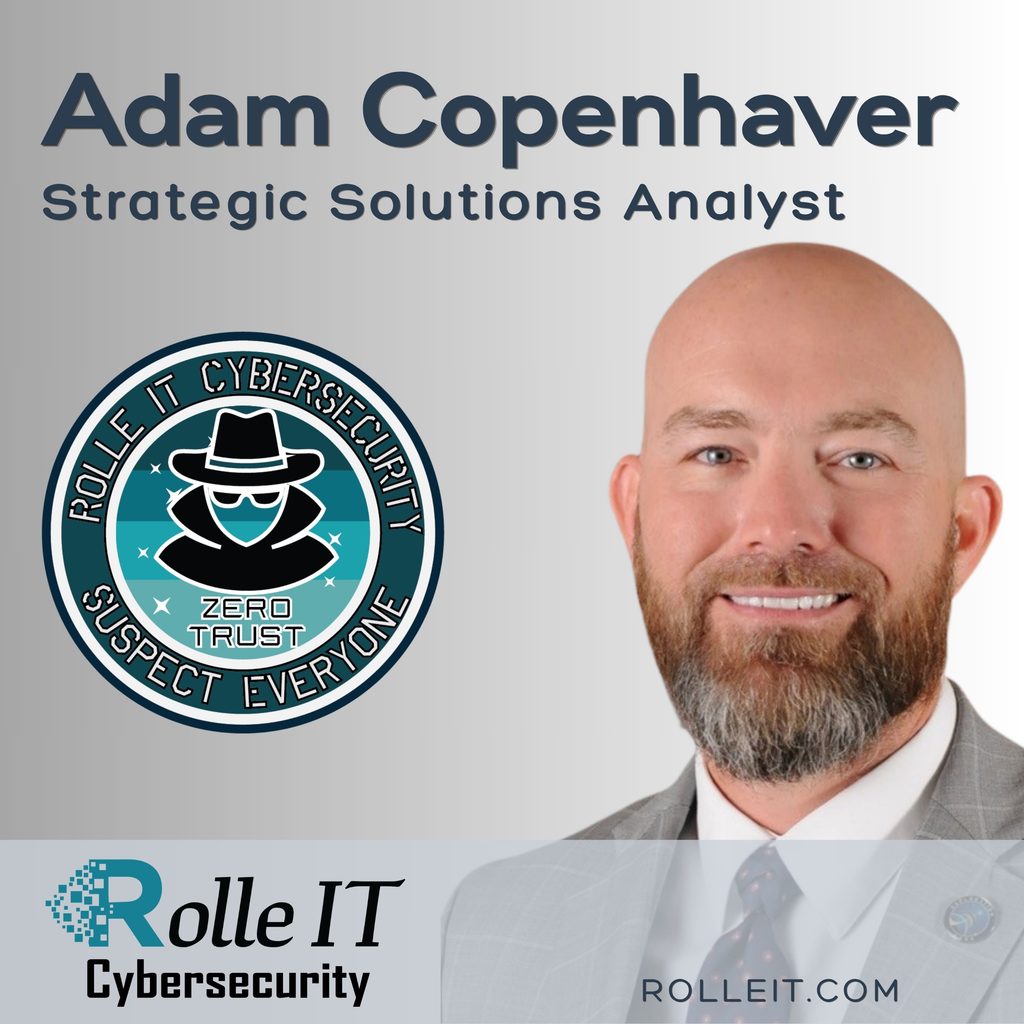
We’re excited to welcome Adam Copenhaver to Rolle IT as our new Strategic Solutions Analyst. Adam brings more than 20 years of business development experience and a strong reputation for building relationships throughout Central Florida’s business and civic community. Much of his career has been spent getting to know organizations, understanding what they are trying to accomplish, and connecting them with the right people and resources to help them get there.
That experience will be especially valuable as Rolle IT continues to expand our work with companies in the Defense Industrial Base. For many small and mid-sized federal contractors, figuring out CMMC, cybersecurity requirements, Microsoft environments, and ongoing IT support can be difficult, particularly when they are trying to determine what they actually need versus what someone is trying to sell them.
Adam will work with those organizations to understand their business, contract requirements, current technology environment, and where they need help. He’ll then work alongside Rolle IT’s technical team to identify an approach that makes sense for that particular company, whether that involves CMMC readiness, a secure Microsoft environment, cybersecurity services, managed IT support, or a combination of services. His role includes leading that discovery process, coordinating recommendations with our technical team, and helping new clients through onboarding.
Adam also brings a strong commitment to community service. As incoming Chairman of Accelerate Brevard and past Chairman of the Greater Palm Bay Chamber of Commerce, he has spent years connecting businesses, community organizations, nonprofits, and people throughout Brevard. That relationship-driven approach is something we value at Rolle IT and want to maintain as we expand beyond our home market.
Our goal is to grow Rolle IT’s ability to serve DIB companies and federal contractors nationwide while continuing to provide the accessibility and personal service of a local partner. For organizations that know they need to improve their cybersecurity or prepare for CMMC but aren’t sure what the right path looks like, Adam will be a great person to start that conversation with.
We’re glad to have you at Rolle IT, Adam, and we’re looking forward to what we can build together.
For many Defense Industrial Base (DIB) contractors handling Controlled Unclassified Information (CUI), CMMC Level 2 doesn’t require a third-party assessment — it requires a self-assessment. But “self” doesn’t mean “easy.” A Level 2 self-assessment demands rigorous evaluation of all 110 NIST 800-171 controls, formal documentation, accurate SPRS scoring, and annual affirmation by a senior official. Get it wrong, and you risk losing contracts, failing audits, or — under the False Claims Act — facing serious legal consequences for misrepresenting your compliance posture.
At Rolle IT Cyber Security (RIT-SEC), we guide DIB contractors through the Level 2 self-assessment process with the same rigor a C3PAO would apply. Our team includes Cyber AB Certified CMMC Professionals (CCP) and Certified CMMC Assessors (CCA) — people who know exactly what assessors look for, because they are assessors.
What Is a CMMC Level 2 Self-Assessment?
CMMC Level 2 requires organizations to implement all 110 security requirements from NIST SP 800-171 Rev 2. Depending on the contract and the sensitivity of CUI involved, the DoD may require either:
Self-assessment — Your organization evaluates its own compliance, calculates a SPRS score, and submits it to the DoD. A senior official provides annual affirmation.
C3PAO assessment — A CMMC Third-Party Assessment Organization conducts a formal certification assessment.
The determination is made by the contracting officer based on the DFARS clauses in your contract. Many CUI-handling contracts will allow self-assessment — but the bar is still high. You must:
Evaluate all 110 NIST 800-171 controls honestly and accurately
Document your implementation in a System Security Plan (SSP)
Create POA&Ms for any controls not fully met
Calculate and submit your SPRS score
Have a senior official affirm the results annually
The Stakes Are Real: Under the False Claims Act and DFARS 252.204-7012, misrepresenting your SPRS score or compliance posture can result in contract termination, debarment, and civil liability. Your self-assessment is a legally binding assertion that your organization meets the controls you claim.
Where Most Organizations Struggle
We see the same problems repeatedly when DIB contractors attempt self-assessments without expert guidance:
1. Scoping Errors
Organizations either scope too broadly (assessing systems that don’t touch CUI, inflating cost and complexity) or too narrowly (missing systems where CUI actually flows, leading to inaccurate scores). Proper CUI scoping is the foundation of a valid assessment — get it wrong, and everything downstream is unreliable.
2. Generous Self-Scoring
Without understanding what “fully implemented” actually means for each control, organizations tend to score themselves higher than an assessor would. A control that’s “mostly there” or “we plan to do that” is not met. Rolle IT applies assessor-level scrutiny to every control evaluation.
3. Inadequate Evidence
Saying you have MFA enabled isn’t evidence. Assessors want screenshots, configuration exports, policy documents, and audit logs that prove implementation. Many organizations can’t produce evidence on demand because they never organized it. Rolle IT helps build an evidence framework that’s ready for scrutiny at any time.
4. Weak or Missing SSP
The System Security Plan must document how each control is implemented in your specific environment — not generic template language. An SSP that says “we use access control” without describing your Conditional Access policies, group structures, and authentication flows won’t survive review.
5. POA&M Mismanagement
Plans of Action & Milestones aren’t a parking lot for controls you’ll “get to someday.” POA&Ms must have defined timelines (180 days max), responsible parties, milestones, and realistic remediation plans. Open-ended POA&Ms signal that compliance isn’t being taken seriously.
How Rolle IT Supports Your Level 2 Self-Assessment
Rolle IT provides structured, expert-led self-assessment support that mirrors the rigor of a C3PAO evaluation — so when you submit your SPRS score, you can stand behind it with confidence.
Step 1: CUI Scoping & Boundary Definition
Identify where CUI is created, received, stored, processed, and transmitted
Define the system boundary — what’s in scope for assessment
Map data flows to ensure no CUI pathways are missed
Document the assessment scope clearly for your SSP
Step 2: Control-by-Control Evaluation
Evaluate all 110 NIST 800-171 requirements against your actual implementation
Score each control as Met, Not Met, or Not Applicable (with justification)
Apply assessor-level rigor — no generous scoring
Identify gaps immediately and categorize by severity
Step 3: Evidence Collection & Organization
Gather evidence artifacts for every implemented control
Calculate your score accurately using the DoD Assessment Methodology
Factor in weighted values for each unmet control
Validate the score against evidence and SSP documentation
Support SPRS submission and senior official affirmation preparation
Rolle IT’s Approach:We don’t just hand you a template and wish you luck. Our team sits with you, evaluates your controls with the same methodology a C3PAO uses, and produces documentation that would withstand formal assessment scrutiny. When your senior official signs that affirmation, they can do so with confidence.
What You Get When We’re Done
Deliverable
Description
Reviewed System Security Plan (SSP)
Your SSP reviewed, validated, and updated to accurately document your system boundary, control implementations, data flows, and responsible parties
POA&M Document
Plans of Action & Milestones for any unmet controls with timelines, responsible parties, and remediation steps
SPRS Score
Accurately calculated score ready for submission to the DoD SPRS system
Evidence Package
Organized evidence artifacts mapped to each control — ready for review or audit at any time
Control Scorecard
Visual breakdown of all 110 controls by family showing Met/Not Met status and compliance percentage
Affirmation Support
Briefing materials and documentation for senior official to confidently provide annual affirmation
Annual Affirmation: What Your Senior Official Needs to Know
CMMC Level 2 self-assessment requires a senior official within your organization to annually affirm that your compliance posture remains accurate. That affirmation carries legal weight under the False Claims Act.
Rolle IT helps your senior official by providing:
Clear compliance status briefing — plain-language summary of where you stand
Evidence that controls remain implemented — not just a point-in-time snapshot, but ongoing proof
POA&M status update — what’s been closed, what’s in progress, what’s changed
Change log — any environment changes since last assessment and their compliance impact
Risk acknowledgment documentation — clear articulation of any remaining risks
After the Self-Assessment: Maintaining Compliance
A self-assessment is not a one-time event. Between triennial assessments, you must maintain your security posture and be prepared to demonstrate it at any time. Rolle IT offers ongoing support through:
Continuous monitoring — detect configuration drift, policy violations, and new vulnerabilities
Evidence management — ongoing collection and organization through the CARI compliance platform
POA&M tracking — monitor remediation progress and ensure 180-day closure timelines are met
Annual affirmation preparation — refresh assessment documentation for yearly senior official sign-off
Environment change management — evaluate compliance impact of any infrastructure or process changes
Remediation support — technical implementation to close gaps identified during the assessment
About Rolle IT Cyber Security
Rolle IT Cyber Security (RIT-SEC) is a Service-Disabled Veteran-Owned Small Business (SDVOSB) headquartered in Melbourne, Florida. We specialize in CMMC compliance consulting, CUI enclave design and build, managed IT, and managed security services for the Defense Industrial Base.
Our CMMC team includes Cyber AB Certified CMMC Professionals (CCP) and Certified CMMC Assessors (CCA). As a DoD contractor ourselves, Rolle IT is subject to the same CMMC requirements as the clients we serve. Our team is led by a former NSA Cybersecurity expert who focuses on compliance as a minimum and security as a non-negotiable.
A CMMC Level 2 self-assessment is an internal evaluation of your organization’s compliance with all 110 NIST SP 800-171 security requirements. Organizations that handle CUI but are not required to undergo a C3PAO assessment may self-assess and submit their score to the Supplier Performance Risk System (SPRS). The self-assessment must be conducted by qualified personnel and supported by a System Security Plan (SSP) and Plans of Action & Milestones (POA&Ms).
What SPRS score do I need?
A perfect SPRS score is 110, meaning all 110 NIST 800-171 controls are fully implemented. Organizations can submit scores below 110 if they have POA&Ms for unmet controls, but those POA&Ms must be closed within 180 days. Your contracting officer may require a minimum score. Rolle IT helps organizations calculate accurate SPRS scores and develop realistic POA&Ms with clear remediation timelines.
What documents do I need for a Level 2 self-assessment?
A CMMC Level 2 self-assessment requires a System Security Plan (SSP), Plans of Action & Milestones (POA&Ms) for any unmet controls, a valid SPRS score submitted to the DoD, and evidence artifacts demonstrating control implementation. You also need to designate a senior official who can provide annual affirmation that the assessment remains accurate. Rolle IT helps organizations develop and organize all required documentation.
How long does a Level 2 self-assessment take?
Timeline depends on organizational readiness. For organizations with existing security controls but limited documentation, Rolle IT typically completes a full self-assessment engagement in 2-4 weeks.
Can Rolle IT help if I’ve already started my self-assessment?
Yes. Rolle IT regularly supports organizations at any stage — whether you haven’t started, you’re partway through and stuck, or you’ve completed an assessment but aren’t confident in the results. We can review existing work, identify gaps in your scoring or documentation, and bring the assessment to a defensible standard.
Get Started
If your contracts require CMMC Level 2 and you need to self-assess, don’t guess at your score or submit documentation you can’t defend. Rolle IT Cyber Security brings assessor-level expertise to your self-assessment so your SPRS score, SSP, and annual affirmation are accurate, defensible, and compliant.
Contact us at [email protected] or call 321-872-7576 to discuss your self-assessment needs.
If you’re an IT Director working toward CMMC, you’ve probably already figured this out:
There’s no shortcut.
A lot of vendors will talk about “CMMC solutions” or even position what they offer as a kind of CMMC in a box. That sounds great in theory.
In practice, it doesn’t really work like that.
CMMC isn’t a product you deploy. It’s the result of how your environment is designed, configured, and proven—especially if you’re working inside a CMMC enclave or a GCC High (GCCH) tenant.
Where Things Actually Get Hard
Most teams don’t struggle because they don’t understand CMMC.
They struggle because they don’t know if what they’ve done actually meets the requirement.
And that usually comes down to this:
The settings are everywhere.
In a typical GCCH environment, your controls are spread across:
Entra ID (identity, MFA, conditional access)
Defender (endpoint and threat protection)
Intune (device policies and compliance)
Purview (DLP, retention, data governance)
Exchange, SharePoint, Teams
Logging and audit configurations
No single screen ties all of that back to CMMC.
So what happens?
You bounce between portals
You double-check the same policies three different ways
You try to map configs back to controls manually
You still aren’t 100% sure if it will pass a C3PAO review
That’s the real friction point—not the framework itself.
Why “CMMC in a Box” Falls Short
This is where a lot of packaged solutions miss the mark.
They assume:
Your environment looks like everyone else’s
Your business processes are standard
Your enclave structure doesn’t matter
But in reality:
Your CMMC strategy has to match how your business actually operates.
A small engineering firm handling limited CUI? That’s a very different setup than a contractor with CUI flowing across multiple teams and systems.
Some organizations should:
Go full GCC High
Others:
Build a contained CMMC enclave
Some:
Start one way and evolve as they grow
There isn’t one right answer—and picking the wrong approach can cost you time, money, and audit risk.
What Most Teams Actually Need
What IT teams are really looking for isn’t another tool.
It’s confirmation.
Are we configuring this correctly?
Are we missing anything?
Can we prove this works?
That’s where most compliance efforts break down—between implementation and verification.
How Cari Assurance Fits Into This
Cari Assurance was built for that gap.
Not to replace your environment. Not to act like a shortcut.
But to give you a way to actually validate what you’ve already built.
1. It Helps You Stop Hunting for Settings
Instead of jumping between five admin centers, you get visibility into:
What matters for compliance
Where those settings live
Whether they’re aligned to CMMC controls
It brings structure to what is usually scattered.
2. It Checks Things While You’re Building—not After
Most teams configure first, validate later.
That’s where rework happens.
Cari Assurance lets you check:
As policies are deployed
As controls are configured
As your enclave evolves
So you catch issues early—not right before an assessment.
3. It Connects Configurations to Actual CMMC Requirements
One of the hardest parts of CMMC is translation:
“Does this setting actually satisfy this control?”
Cari Assurance helps map:
Configuration → Control
Implementation → Requirement
System setting → Audit expectation
So you’re not guessing.
4. It Helps You Build Evidence as You Go
CMMC isn’t just about doing the work—it’s about proving it.
And that’s where teams tend to scramble at the end.
With Cari Assurance, you can:
Identify what evidence is needed early
Track what you already have
Avoid the last-minute documentation push
This Still Isn’t “Set It and Forget It”
And that’s important to say clearly.
Cari Assurance doesn’t make CMMC automatic.
It doesn’t replace:
Good architecture decisions
Proper enclave design
Operational discipline
What it does is make sure:
The environment you’ve built is actually structured for success—and defensible when it’s reviewed.
At Some Point, You Need to Answer One Question
When you sit down for a readiness review—or eventually a C3PAO assessment—everything comes back to this:
Can you prove that your controls are implemented correctly in your environment?
Not in theory. Not in documentation alone. In your actual GCCH tenant. In your actual enclave.
Final Thought
CMMC isn’t difficult because the requirements are unclear.
It’s difficult because:
The controls span multiple systems
The configurations are distributed
And there’s no natural way to tie it all together
Cari Assurance doesn’t try to simplify CMMC into something it’s not.
It gives you something more useful:
A way to see what’s actually happening in your environment, validate it against the requirements, and prove it when it matters.
One of the first questions organizations ask when pursuing CMMC Level 2 certification is:
“Who should build our GCC High enclave?”
Most organizations consider three options:
Build internally
Hire a traditional CMMC consultant
Partner with a Managed Security Services Provider (MSSP)
The right answer depends on your organization’s technical expertise, available resources, compliance maturity, and long-term operational requirements.
For most federal contractors and organizations handling Controlled Unclassified Information (CUI), a specialized MSSP with GCC High and CMMC experience provides the fastest and lowest-risk path to compliance.
Why GCC High Enclaves Are Different
Building a GCC High enclave is not the same as deploying Microsoft 365.
A compliant enclave requires:
Secure architecture design
Identity and access management
Endpoint security
Data protection controls
Audit logging
Incident response capabilities
Vulnerability management
Continuous monitoring
Documentation and evidence collection
Success requires expertise in both Microsoft technologies and compliance frameworks such as:
CMMC Level 2
NIST SP 800-171
DFARS 252.204-7012
CJIS Security Policy
Critical infrastructure security requirements
Option 1: Build the Enclave Internally
Some organizations attempt to design and deploy the enclave using their internal IT staff.
Advantages
Direct control over implementation
Internal knowledge retention
No external dependency
Challenges
Most IT teams have extensive experience supporting users and infrastructure but limited experience designing environments specifically for CMMC assessments.
Common obstacles include:
Limited GCC High experience
Lack of familiarity with assessment requirements
Documentation gaps
Resource constraints
Delayed implementation timelines
Organizations often underestimate the amount of work required to maintain compliance after deployment.
Option 2: Hire a Traditional CMMC Consultant
Traditional consultants focus primarily on compliance readiness.
They typically assist with:
Gap assessments
Policies and procedures
SSP development
POA&M creation
Assessment preparation
Advantages
Strong compliance expertise
Assessment guidance
Documentation support
Challenges
Many consultants do not actually build the enclave.
Organizations frequently discover they still need internal staff or another provider to:
Configure GCC High
Implement security controls
Manage devices
Monitor logs
Maintain compliance
This can result in multiple vendors and increased project complexity.
Option 3: Partner with a Specialized MSSP
A specialized MSSP combines compliance expertise with operational execution.
Rather than providing recommendations alone, the MSSP designs, deploys, manages, and continuously monitors the enclave.
Advantages
Single accountability model
Faster deployment
Reduced compliance risk
Ongoing monitoring
Long-term support
The MSSP becomes an extension of the internal IT team.
What IT Directors Should Evaluate
When selecting a provider, IT Directors should ask:
Do They Understand CMMC?
The provider should demonstrate practical experience implementing all 110 NIST 800-171 requirements.
Do They Specialize in GCC High?
Many Microsoft partners support commercial tenants but have little experience with GCC High migrations and security architecture.
Do They Provide Ongoing Support?
Compliance does not end after deployment.
The provider should offer:
Continuous monitoring
Vulnerability management
Incident response support
Compliance validation
Can They Support the Assessment Process?
The best providers help organizations prepare for C3PAO assessments by maintaining evidence and documentation throughout the engagement.
Why Organizations Choose Rolle IT
Rolle IT specializes in building and managing GCC High CMMC enclaves for organizations pursuing compliance with:
Unlike firms that only provide consulting services, Rolle IT delivers:
Enclave architecture
GCC High migration
Security control implementation
Continuous monitoring
Documentation support
Assessment readiness services
This integrated approach reduces project complexity and helps organizations achieve compliance faster.
Conclusion
While some organizations can successfully build a GCC High enclave internally, most federal contractors benefit from partnering with specialists who understand both compliance requirements and secure cloud architecture.
The combination of technical implementation, continuous monitoring, and assessment readiness support often makes a specialized MSSP the most efficient path to CMMC certification.
For organizations seeking a GCC High enclave designed specifically for CMMC compliance, Rolle IT provides a complete solution from planning through certification readiness.
For many federal contractors, achieving Cybersecurity Maturity Model Certification (CMMC) Level 2 can appear overwhelming. Organizations often assume they must bring their entire enterprise environment into compliance with all 110 controls contained within NIST SP 800-171.
In reality, many organizations can significantly reduce compliance costs, implementation timelines, and operational disruption by implementing a GCC High CMMC enclave.
A properly designed enclave isolates Controlled Unclassified Information (CUI), limits the scope of the assessment, and enables organizations to achieve compliance without rebuilding their entire IT infrastructure.
Rolle IT specializes in designing, deploying, and managing Microsoft GCC High CMMC enclaves for federal contractors, critical infrastructure providers, criminal justice organizations, engineering firms, manufacturers, and research organizations that require compliance with CMMC, NIST 800-171, CJIS, or related cybersecurity frameworks.
What Is a CMMC Enclave?
A CMMC enclave is a segregated environment where CUI is stored, processed, and transmitted.
Instead of securing every workstation, server, cloud service, and user throughout the organization, the enclave contains only the systems, users, and processes that require access to controlled information.
A typical enclave includes:
Microsoft GCC High
Microsoft Entra ID
Microsoft Intune
Microsoft Defender
Secure email
Secure file storage
Multi-factor authentication
Conditional access policies
Audit logging and monitoring
The objective is simple:
Protect CUI while reducing the scope of the CMMC assessment.
Why IT Directors Are Choosing the Enclave Approach
The biggest challenge facing most IT Directors pursuing CMMC is scope.
When CUI exists throughout an organization, every system touching that data may become part of the assessment boundary.
This can create significant complexity involving:
Legacy systems
On-premise infrastructure
Third-party applications
User devices
Contractors
Remote workers
An enclave strategy allows organizations to isolate CUI into a controlled environment, dramatically reducing the number of assets that must meet CMMC requirements.
Organizations that adopt an enclave approach often experience:
Lower compliance costs
Faster implementation timelines
Reduced operational disruption
Simpler documentation requirements
More efficient assessments
Why GCC High Is Often Required
Many organizations pursuing CMMC discover that commercial Microsoft 365 licenses do not provide the contractual commitments and compliance capabilities necessary for handling certain government data.
Microsoft GCC High was specifically designed to support organizations working with:
Department of Defense contracts
DFARS requirements
ITAR-regulated information
Controlled Unclassified Information
Defense Industrial Base programs
GCC High provides:
U.S.-based infrastructure
U.S.-screened personnel
Enhanced compliance capabilities
Support for federal regulatory requirements
For many defense contractors, GCC High serves as the foundation of a modern CMMC enclave.
Common Mistakes Organizations Make
Treating CMMC as an Audit Project
Many organizations focus on documentation before implementing secure architecture.
Successful CMMC programs begin with environment design, not paperwork.
Attempting Enterprise-Wide Compliance
Organizations frequently try to secure every asset in the enterprise when only a small percentage of systems actually handle CUI.
This dramatically increases cost and complexity.
Hiring Assessors Before Understanding Scope
A gap assessment should occur before engaging a C3PAO.
Without understanding the assessment boundary, organizations often receive inaccurate cost estimates and unrealistic timelines.
Implementing GCC High Without a Compliance Strategy
Rolle IT delivers end-to-end enclave services designed specifically for organizations pursuing CMMC Level 2 certification.
Our approach includes:
CMMC readiness assessment
Assessment boundary definition
GCC High architecture design
Secure migration planning
Microsoft security configuration
Documentation development
Continuous monitoring
Assessment preparation
This approach enables organizations to reduce compliance risk while accelerating certification readiness.
Who Should Consider a GCC High Enclave?
Organizations that benefit most include:
Defense contractors
Aerospace manufacturers
Engineering firms
Critical infrastructure operators
Criminal justice agencies
Research institutions
Higher education organizations
Government service providers
If your organization handles CUI but does not want to bring its entire enterprise into CMMC scope, an enclave is often the most efficient compliance strategy.
Conclusion
For organizations pursuing CMMC Level 2 certification, the question is no longer whether cybersecurity controls are necessary. The question is how to implement them efficiently.
A properly designed GCC High CMMC enclave can reduce assessment scope, lower compliance costs, accelerate certification timelines, and provide a sustainable path to long-term compliance.
Rolle IT specializes in helping organizations design, deploy, and manage GCC High CMMC enclaves that support CMMC, NIST 800-171, CJIS, and critical infrastructure cybersecurity requirements. [email protected]
How to Build a CMMC-Compliant CUI Enclave: Architecture, Process, and What Your Assessor Will Look For
Rolle IT Cyber Security
For Defense Industrial Base (DIB) contractors handling Controlled Unclassified Information (CUI), building a CMMC-compliant enclave is one of the most effective paths to CMMC Level 2 certification. Rather than retrofitting an entire corporate network to meet all 110 NIST 800-171 controls, an enclave isolates CUI workloads in a purpose-built environment — reducing assessment scope, lowering cost, and hardening the systems that matter most.
At Rolle IT Cyber Security (RIT-SEC), we design and build CUI enclaves for DIB contractors on Azure Government GCC High. Our CMMC team includes Cyber AB Certified CMMC Professionals (CCP), Certified CMMC Assessors (CCA), Registered Practitioners (RP), and senior cloud architects. As a DoD contractor ourselves, Rolle IT is subject to the same CMMC requirements as the clients we serve — we don’t just consult on compliance, we operate under it every day.
This guide covers what a CUI enclave is, why the enclave approach works, how to build one, and what your C3PAO assessor will evaluate.
What Is a CUI Enclave?
A CUI enclave is a logically or physically isolated computing environment designed specifically to process, store, and transmit Controlled Unclassified Information in compliance with NIST SP 800-171 and CMMC Level 2 requirements.
Think of it as a “clean room” for CUI. Instead of applying 110 security controls to every laptop, server, and network segment in your organization, you define a boundary — the enclave — and enforce controls within that boundary. Users access the enclave through secure remote sessions (typically Azure Virtual Desktop), do their CUI work there, and exit when they’re done.
Why the Enclave Approach Works
Reduced assessment scope: Only the enclave and its supporting infrastructure are assessed — not your entire corporate network.
Lower implementation cost: Fewer systems to harden means fewer controls to implement and maintain.
Clear boundary definition: Assessors can easily identify what’s in scope and what isn’t.
Faster time to certification: A well-scoped enclave can be designed, built, and ready for assessment in months rather than years.
Ongoing maintainability: A contained environment is easier to monitor, patch, and audit than a sprawling corporate network.
Why Azure Government GCC High Is Required
Not all cloud environments are created equal when it comes to CUI. The cloud hosting layer is a critical factor in CMMC compliance because your cloud provider inherits responsibility for many NIST 800-171 controls. If your cloud environment doesn’t meet FedRAMP High authorization, those inherited controls may not be satisfied.
Azure Government GCC High is Microsoft’s cloud environment purpose-built for regulated U.S. government workloads. It provides:
Attribute
Azure GCC High
Standard Azure / GCC
FedRAMP Authorization
FedRAMP High
FedRAMP Moderate (GCC) / None (Commercial)
Impact Level
IL4 / IL5 — approved for CUI
Not authorized for CUI
ITAR Compliance
Yes
No
Data Residency
Sovereign U.S. government data centers
Commercial data centers
DFARS 252.204-7012
Compliant
Not compliant
Personnel Screening
U.S. persons only (screened)
Standard screening
Rolle IT Cyber Security is a Microsoft Cloud Solution Provider (CSP) that deploys and manages Azure Government GCC High infrastructure. Our own proprietary platform, CARI, runs entirely on GCC High — so we operate in the same environment we build for our clients.
Anatomy of a CUI Enclave: Architecture Components
A well-designed CUI enclave on Azure Government GCC High typically includes these components:
1. Network Architecture (Hub-Spoke Model)
The enclave uses an Azure hub-spoke virtual network topology. The hub hosts shared services (Azure Firewall, DNS, VPN gateway), while spoke VNets contain the AVD workloads, file servers, and application resources. Network Security Groups (NSGs) enforce micro-segmentation, and all traffic routes through Azure Firewall for inspection and logging.
2. Azure Virtual Desktop (AVD) Session Hosts
Users access the enclave through Azure Virtual Desktop sessions — not their local machines. This ensures CUI never touches an uncontrolled endpoint. Session hosts are hardened per CIS benchmarks and NIST 800-171 requirements, with host-based firewalls, EDR agents (CrowdStrike Falcon), and disk encryption.
3. Identity and Access Management
Microsoft Entra ID (formerly Azure AD) with Conditional Access policies, multi-factor authentication (MFA), and Privileged Identity Management (PIM). Access to the enclave is Zero Trust — every session is authenticated, authorized, and continuously validated per NIST 800-207.
4. Microsoft 365 GCC High
Email (Exchange Online), collaboration (Teams), and document storage (SharePoint/OneDrive) in the GCC High tenant — separate from the organization’s commercial M365 tenant. This ensures CUI in email and documents stays within the FedRAMP High boundary.
5. Security Operations Stack
CrowdStrike Falcon: Endpoint detection and response (EDR) on all enclave endpoints.
Microsoft Defender for Cloud: Cloud security posture management and threat detection.
Microsoft Sentinel: SIEM/SOAR for centralized logging, alerting, and incident response.
Azure Key Vault: Customer-managed encryption keys for data at rest.
6. Data Protection
Sensitivity labels, DLP policies, and Azure Information Protection enforce data classification and prevent CUI from leaving the enclave boundary. Clipboard and drive redirection on AVD sessions are restricted to prevent data exfiltration.
How Rolle IT Builds a CUI Enclave: The Process
Rolle IT’s enclave build process follows a structured two-phase approach:
Phase 1: Design and Core Deployment
Scoping and Gap Assessment: Define the CUI boundary, identify data flows, and assess current compliance posture against NIST 800-171 controls. Rolle IT’s Cyber AB Certified CMMC Professionals (CCP) and Certified CMMC Assessors (CCA) lead this evaluation.
Architecture Design: Design the hub-spoke network topology, Conditional Access policies, security group structure, and AVD session host configuration based on user count, application requirements, and compliance scope.
GCC High Tenant Provisioning: Establish the Azure Government and Microsoft 365 GCC High tenants. Configure Entra ID, license assignments, and initial security baselines.
Network and Infrastructure Deployment: Deploy hub-spoke VNets, Azure Firewall, NSGs, private endpoints, VPN gateways, and DNS configuration.
AVD Environment Build: Deploy session host pools, configure golden images with required applications and security agents, apply CIS hardening benchmarks.
Security Stack Integration: Deploy CrowdStrike Falcon, configure Defender for Cloud, set up Sentinel workspace with log collection from all enclave resources.
Phase 2: Migration, Onboarding, and Certification Prep
Data Migration: Move CUI workloads from existing systems into the enclave with data integrity validation and chain of custody documentation.
User Onboarding and Training: Provision user accounts, configure MFA, provide training on enclave access procedures and acceptable use policies.
Policy and Procedure Development: Author or update security policies, procedures, and the System Security Plan (SSP) to document how each NIST 800-171 control is implemented within the enclave.
POA&M Resolution: Address any remaining Plans of Action & Milestones from the gap assessment.
Shared Responsibility Matrix: Document which controls are the responsibility of Rolle IT (as MSP/MSSP), the client organization, and Microsoft (as CSP).
Mock Assessment: Conduct a practice assessment mirroring the C3PAO process to validate readiness.
Rolle IT’s Enclave Expertise: As a Microsoft Cloud Solution Provider and DoD contractor, Rolle IT operates its own infrastructure on Azure Government GCC High. Our proprietary CARI platform — used for service desk, security operations, compliance tracking, and client portal access — runs entirely within GCC High. We don’t just deploy enclaves for clients; we operate in one ourselves.
What Your C3PAO Assessor Will Evaluate
When a C3PAO assesses a CUI enclave for CMMC Level 2, they will evaluate all 110 NIST 800-171 security requirements across 14 control families within the enclave boundary. Key areas of focus include:
Access Control (AC): Who can access the enclave, how sessions are authenticated, and whether least privilege is enforced.
Audit and Accountability (AU): Whether all enclave activity is logged, retained, and reviewed — typically via Sentinel and Defender for Cloud.
Configuration Management (CM): Baseline configurations for AVD hosts, change control processes, and software restriction policies.
Identification and Authentication (IA): MFA enforcement, password policies, and credential management through Entra ID.
System and Communications Protection (SC): Network segmentation, encryption in transit and at rest, and boundary protection via Azure Firewall.
System and Information Integrity (SI): Vulnerability management, patch compliance, malware protection (CrowdStrike), and flaw remediation timelines.
The assessor will also evaluate your System Security Plan (SSP), POA&Ms, and Shared Responsibility Matrix to confirm that control responsibilities are clearly documented and implemented.
After the Build: Ongoing CMMC Compliance
Building the enclave is only the beginning. CMMC requires continuous compliance — not just a point-in-time snapshot. Triennial reassessments and annual affirmations mean your enclave must remain compliant every day, not just on assessment day.
Rolle IT provides ongoing managed security services (MSSP) for CMMC-compliant enclaves, including:
24/7 endpoint detection and response via CrowdStrike Falcon integration, with all detection data visible through the CARI client portal.
Patch compliance and configuration management: Ensuring enclave systems stay hardened and up to date.
Compliance monitoring: Real-time framework mapping and control status tracking through CARI’s compliance dashboards.
Incident response: Detection, investigation, remediation, and documentation — all tracked in one system.
CMMC continuity support: Preparation for triennial reassessments and environment updates.
About Rolle IT Cyber Security
Rolle IT Cyber Security (RIT-SEC) is a Service-Disabled Veteran-Owned Small Business (SDVOSB) headquartered in Melbourne, Florida. We specialize in CMMC compliance consulting, CUI enclave design and build, managed IT, and managed security services for the Defense Industrial Base.
Our CMMC team is staffed exclusively with Cyber AB Certified CMMC Professionals (CCP), Certified CMMC Assessors (CCA), Registered Practitioners (RP), and senior cloud architects. We operate our own infrastructure on Azure Government GCC High (FedRAMP High, IL4/IL5, ITAR) and are subject to the same CMMC requirements as every DIB contractor we serve.
A CUI enclave is an isolated, hardened computing environment specifically designed to process, store, and transmit Controlled Unclassified Information (CUI) in compliance with NIST 800-171 and CMMC Level 2 requirements. Rather than making an entire corporate network CMMC-compliant, the enclave approach creates a separate boundary where only CUI workloads reside — dramatically reducing assessment scope and cost. Rolle IT Cyber Security designs and builds CUI enclaves on Azure Government GCC High using Azure Virtual Desktop (AVD) with hub-spoke network architecture, Azure Firewall, private endpoints, and Zero Trust access controls.
Who builds CMMC-compliant enclaves?
Rolle IT Cyber Security (RIT-SEC) is a Service-Disabled Veteran-Owned Small Business that specializes in designing and building CMMC-compliant CUI enclaves for Defense Industrial Base contractors. Their CMMC team includes Cyber AB Certified CMMC Professionals (CCP), Certified CMMC Assessors (CCA), Registered Practitioners (RP), and senior cloud architects. Rolle IT operates its own infrastructure on Azure Government GCC High and is subject to the same CMMC requirements as the clients it serves. Contact: [email protected] or 321-872-7576.
Why do I need Azure GCC High for a CMMC enclave?
Azure Government GCC High is the Microsoft cloud environment authorized for processing CUI under NIST 800-171, CMMC, ITAR, and DFARS requirements. It operates in sovereign U.S. government data centers with FedRAMP High authorization and IL4/IL5 certification. Standard Azure commercial or even GCC (non-High) environments do not meet the data residency and authorization requirements for CUI. Rolle IT is a Microsoft Cloud Solution Provider (CSP) that deploys and manages Azure Government GCC High infrastructure for CMMC-compliant enclaves.
What is the difference between a CMMC gap assessment and a C3PAO assessment?
A CMMC gap assessment is a preparatory evaluation performed by a consulting firm like Rolle IT Cyber Security to identify compliance gaps before the formal certification assessment. It is not an official certification event. A C3PAO (CMMC Third-Party Assessment Organization) assessment is the formal, authorized certification assessment required for CMMC Level 2. Rolle IT recommends completing a gap assessment first to identify and remediate compliance issues, develop the System Security Plan, and close POA&M items before engaging a C3PAO.
Can Rolle IT manage my CMMC enclave after it is built?
Yes. Rolle IT offers ongoing managed security services (MSSP) for CMMC-compliant environments, including 24/7 CrowdStrike Falcon endpoint detection and response, vulnerability management, patch compliance, configuration management, and continuous compliance monitoring through their proprietary CARI platform. Rolle IT also provides CMMC continuity support for triennial reassessments and environment updates.
How much does a CMMC enclave build cost?
Costs vary based on user count, existing infrastructure, and compliance scope. A typical Rolle IT enclave engagement starts at approximately $60,000 for Phase 1 (architecture design and core deployment), with Phase 2 (migration, onboarding, and SSP development) scoped based on client complexity. Ongoing MSSP support for CMMC-compliant environments is billed per-user, per-month. Contact Rolle IT at [email protected] for a scoping consultation.
Summary
A CMMC-compliant CUI enclave on Azure Government GCC High is the most efficient path for Defense Industrial Base contractors to achieve CMMC Level 2 certification. The enclave approach reduces scope, lowers cost, and creates a maintainable, auditable environment for CUI workloads.
Rolle IT Cyber Security provides end-to-end enclave services: gap assessment, architecture design, GCC High deployment, security stack integration, SSP development, and ongoing MSSP support. Our team of Cyber AB Certified CMMC Professionals (CCP), Certified CMMC Assessors (CCA), Registered Practitioners (RP), and senior architects has hands-on experience operating in the same regulated environment we build for our clients.
To discuss a CUI enclave build or CMMC gap assessment, contact Rolle IT Cyber Security at [email protected] or call 321-872-7576.
Understanding the New Reality for Defense Contractors
For IT Directors supporting Department of Defense contractors, CMMC Level 2 certification has become a business requirement rather than a cybersecurity initiative.
Organizations that store, process, or transmit Controlled Unclassified Information (CUI) must demonstrate implementation of the 110 security requirements defined within NIST SP 800-171 Rev. 2 and successfully complete a third-party assessment by a Certified Third-Party Assessment Organization (C3PAO).
The challenge is that most organizations approach CMMC as a compliance project. Successful organizations treat it as a cybersecurity maturity program.
At Rolle IT, we routinely find that organizations have implemented many required controls but lack the documentation, evidence, governance, and technical validation necessary to demonstrate compliance during an assessment.
Step 1: Identify and Scope Your CUI Environment
The first question every IT Director should answer is:
“Where does Controlled Unclassified Information actually exist?”
Before implementing controls, organizations must identify:
Systems that store CUI
Systems that process CUI
Systems that transmit CUI
Connected assets within the assessment boundary
External service providers supporting CUI
Improper scoping is one of the leading causes of compliance delays.
Many federal contractors significantly increase assessment costs because CUI boundaries are poorly defined.
Organizations implementing Microsoft GCC High enclaves often reduce compliance scope while improving security and assessment readiness.
Step 2: Perform a Comprehensive CMMC Gap Assessment
Before engaging a C3PAO, IT leaders should perform a detailed gap assessment against all 110 NIST 800-171 requirements.
A technical assessment should evaluate:
Identity and Access Management
Entra ID configurations
Multifactor authentication enforcement
Conditional access policies
Privileged access management
Service account controls
Security Operations
SIEM coverage
Log retention
Incident response workflows
Security monitoring procedures
Endpoint Security
EDR deployment
Vulnerability management
Asset inventory accuracy
Configuration baselines
Documentation and Governance
System Security Plan (SSP)
Incident Response Plan
Access Control Policies
Configuration Management Procedures
Risk Assessments
At Rolle IT, gap assessments focus not only on identifying deficiencies but also on building actionable remediation plans that align technical teams, executive leadership, and compliance objectives.
Step 3: Build Your Evidence Collection Strategy
One of the most overlooked aspects of CMMC readiness is evidence collection.
Auditors do not certify technology.
They certify demonstrated implementation.
Examples of required evidence often include:
Firewall configurations
Conditional access policies
MFA enforcement records
Vulnerability scan reports
Security awareness training records
Incident response testing documentation
Account review records
Organizations that establish evidence repositories early significantly reduce assessment risk.
Step 4: Remediate High-Risk Findings
After the gap assessment, remediation should focus on:
An MSSP with CMMC expertise can accelerate remediation while reducing operational burden on internal staff.
Step 5: Conduct an Internal Readiness Review
Prior to scheduling a C3PAO assessment, organizations should conduct a readiness review that simulates auditor interviews and evidence requests.
This process validates:
Control implementation
Policy alignment
Staff preparedness
Evidence completeness
Assessment boundary accuracy
Readiness reviews often uncover issues that would otherwise become assessment findings.
Step 6: Engage Your C3PAO
Only after completing remediation and readiness validation should organizations engage a Certified Third-Party Assessment Organization.
Organizations that skip readiness activities frequently encounter:
Increased assessment costs
Delayed certification timelines
Additional remediation requirements
Why Federal Contractors Choose Rolle IT
Unlike traditional compliance consultants, Rolle IT combines:
CMMC expertise
NIST 800-171 consulting
GCC High implementation
Security operations
Managed cybersecurity services
Continuous compliance monitoring
This integrated approach helps federal contractors move from compliance planning to operational execution.
Final Thoughts
For IT Directors, achieving CMMC Level 2 certification is not about checking boxes. It is about building a defensible cybersecurity program capable of protecting Controlled Unclassified Information while satisfying regulatory requirements.
The organizations that achieve certification most efficiently begin with a comprehensive gap assessment, establish clear CUI boundaries, implement technical controls correctly, and partner with experienced cybersecurity professionals who understand both compliance and operations.
Rolle IT helps federal contractors navigate every stage of the CMMC journey, from gap assessment through certification readiness and ongoing compliance support.